Vulnerability Risk-Acceptance Engine
Python · GitHub Actions · CrowdStrike Spotlight · Vanta · CISA KEV
During my internship at ElevateBio, I was asked to automate risk acceptance ahead of an ISO 27001 audit. I had the acceptance criteria and a rough scope. My manager's first plan was to configure an enterprise AI agent to make the decisions and write the reports.
After weeks of trial and error, reading documentation and blog posts, and debugging, I came to a different conclusion. The point was to pass an audit, and an auditor has to trace every accepted risk back to the reasoning behind it. Code gives you that line by line. An agent's output is much harder to defend. I pitched a programmatic design to a senior security officer, he agreed, and I built it.
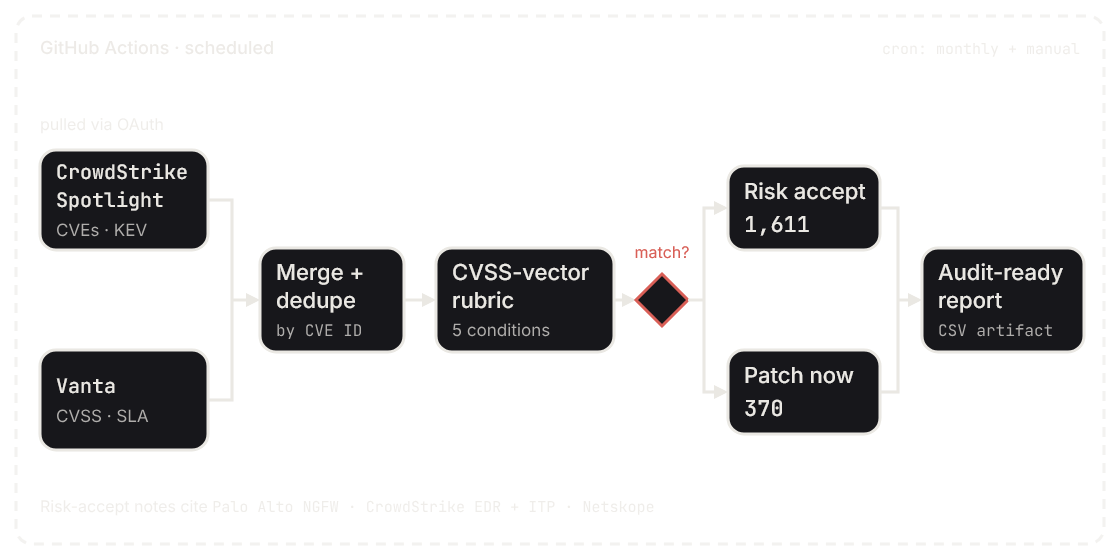
The pipeline pulls findings from CrowdStrike Spotlight and Vanta, deduplicates by CVE, scores each one against a CVSS-vector rubric, and writes a justification naming the compensating control. It cleared 1,611 vulnerabilities before the audit and flagged 370 for patching. It runs on a schedule, and the company still uses it. The AI did end up in the project, just where it fit: an assistant on top that lets engineers ask about their posture in plain English.